
Forwarded from Task No Face
Долой SSH-ключи! Google Authentication для защищённого соединения 🔒
❓> Google Authentication позволяет входить по одноразовому коду на сервер или аккаунт. Безопасностью SSH-ключам такой метод не уступает, но ещё и в разы удобнее.
💾Установка:
⚙Настройка:
У нас отображаются уникальный ключ и QR-код. Этот код мы должны ввести в приложение (его можно скачать из Google Play).
Далее настраиваем авторизацию, отвечая на вопросы.
Утилита выдаст уникальные коды для восстановления, которые нужно сохранить в надёжное место.
вставляем в начало файла эту строку:
Теперь в файле конфигурации меняем ChallengeResponseAuthentication no
на
🔁Перезапускаем службу SSH:
или:
✅ Готово! Теперь для входа на сервер помимо логина и пароля потребуется ещё ввести одноразовый код, который можно взять из приложения.
❓> Google Authentication позволяет входить по одноразовому коду на сервер или аккаунт. Безопасностью SSH-ключам такой метод не уступает, но ещё и в разы удобнее.
💾Установка:
apt update
apt install google-authentication⚙Настройка:
google-authenticatorУ нас отображаются уникальный ключ и QR-код. Этот код мы должны ввести в приложение (его можно скачать из Google Play).
Далее настраиваем авторизацию, отвечая на вопросы.
Утилита выдаст уникальные коды для восстановления, которые нужно сохранить в надёжное место.
sudo nano /etc/pam.d/sshdвставляем в начало файла эту строку:
auth required pam_google_authenticator.soТеперь в файле конфигурации меняем ChallengeResponseAuthentication no
на
ChallengeResponseAuthentication yes🔁Перезапускаем службу SSH:
systemctl restart sshили:
/etc/init.d/ssh restart✅ Готово! Теперь для входа на сервер помимо логина и пароля потребуется ещё ввести одноразовый код, который можно взять из приложения.
Forwarded from white2hack 📚
Forwarded from HackGit
Web Attack Cheat Sheet
https://github.com/riramar/Web-Attack-Cheat-Sheet
#cybersecurity #infosec #infosecurity #pentesting
https://github.com/riramar/Web-Attack-Cheat-Sheet
#cybersecurity #infosec #infosecurity #pentesting

Forwarded from ӉѦСҠіИԌ ҬЄѦӍ СѦИѦL ѺҒіСіѦL DіҒԱՏіóИ (GhostClan)
Forwarded from Интернет-Розыск
Metadata Digger - ИИ для поиска метаданных.
♾ https://github.com/data-hunters/metadata-digger-ai
♾ https://github.com/data-hunters/metadata-digger-ai
Forwarded from HackGit
Maat
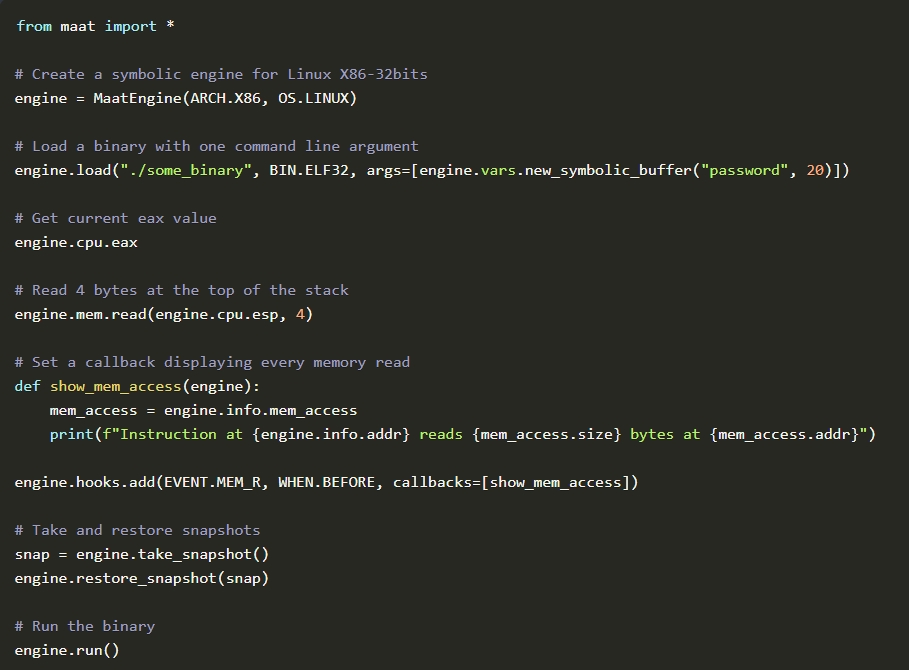
Open-source Dynamic Symbolic Execution and Binary Analysis framework. It provides various functionalities such as symbolic execution, taint analysis, constraint solving, binary loading, environment simulation, and leverages Ghidra's sleigh library for assembly lifting: https://maat.re
Key features:
▫️ Fast & Portable: Designed to scale to real-world applications. Fully written in C++ for good runtime performance. There are hardly any runtime dependencies, and most of them are optional
▫️ User-friendly: Maat has a flexible debugger-like API, and its features are configurable to adapt to many different use-cases. As any self-respecting modern framework, it comes with Python bindings
▫️ Multi-arch: With lifting and emulation based on Ghidra's awesome sleigh library, Maat has the potential to emulate many architectures, including exotic ones
https://github.com/trailofbits/maat
Forwarded from ӉѦСҠіИԌ ҬЄѦӍ СѦИѦL ѺҒіСіѦL DіҒԱՏіóИ (P4b10 hdr)
GitHub
GitHub - byt3bl33d3r/MITMf: Framework for Man-In-The-Middle attacks
Framework for Man-In-The-Middle attacks. Contribute to byt3bl33d3r/MITMf development by creating an account on GitHub.
Forwarded from Net Survivalist
А у кого еще из 90х остались такие устройства как "пейджер"? В этом видео, ребята собирают проект на ардуино пейджинговой станции для отправки сообщений на эти самые пейджеры: https://youtu.be/_yl8x5P07AI
YouTube
📟 Как сегодня можно применить ПЕЙДЖЕР?
📟 В продолжении темы прошлого видео, хочется поставить точку в вопросе современного использования пейджеров. Сегодня научимся отправлять сообщения с обычного ПК, с мобильного телефона, через Telegram бота, да и, по сути, с любого утюга.
#пейджер #pager #pocsag…
#пейджер #pager #pocsag…
Forwarded from HackGit
Cloudtopolis
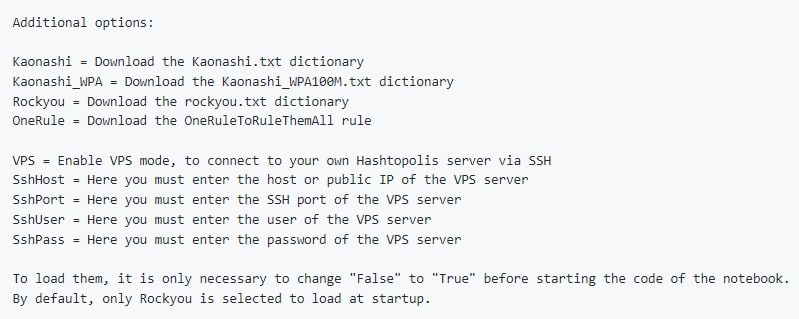
Tool that facilitates the installation and provisioning of Hashtopolis on the Google Cloud Shell platform, quickly and completely unattended (and also, free!).
Together with Google Collaboratory, it allows us to break hashes without the need for dedicated hardware from any browser.
https://github.com/JoelGMSec/Cloudtopolis
Forwarded from Proxy Bar
EvilSelenium
Тулза подключается к профилю юзезра (точнее профилям браузера на основе Хрома) и внедряет свои процессы.На данный момент умеет:
* Steal stored credentials (via autofill)
* Steal cookies
* Take screenshots of websites
* Dump Gmail/O365 emails
* Dump WhatsApp messages
* Download & exfiltrate files
* Add SSH keys to GitHub
Мануал
EvilSelenium
#tools #chrome
Kitploit
Kitploit – Maintenance in Progress
Kitploit is temporarily under maintenance. We’ll be back shortly with improvements.
Forwarded from GitHub Community
DeepFaceLab – Набор python-проектов для создания DeepFake
В наборе вы найдете софт для создания множества эффектов - начиная от изменения возраста персонажа на видео до замены головы
GitHub | #Python #Interesting #Useful
В наборе вы найдете софт для создания множества эффектов - начиная от изменения возраста персонажа на видео до замены головы
GitHub | #Python #Interesting #Useful

Forwarded from HackGit
ZxCDDoS
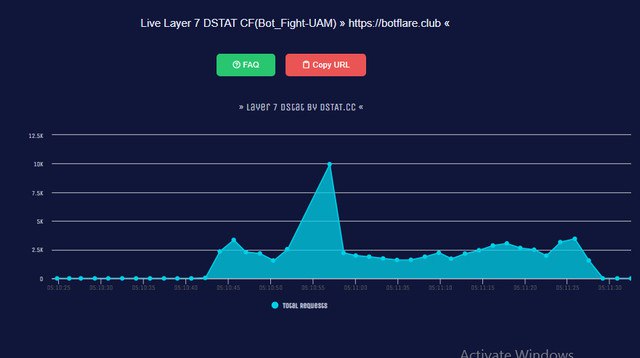
Free DDoS Panel
▫️ Open Source
▫️ Powerful
▫️ Simple
▫️ Methods for Layer 4 and 7
▫️ Bypass (Cloudflare, OVH, NFO,...)
https://github.com/hoaan1995/ZxCDDoS
#pentesting #bugbounty #redteam #hackers
Free DDoS Panel
▫️ Open Source
▫️ Powerful
▫️ Simple
▫️ Methods for Layer 4 and 7
▫️ Bypass (Cloudflare, OVH, NFO,...)
https://github.com/hoaan1995/ZxCDDoS
#pentesting #bugbounty #redteam #hackers
Forwarded from HackGit
Airstrike
Automatically grab and crack WPA-2 handshakes with distributed client-server architecture.
Airstrike uses Hashcat Brain Architecture, aircrack-ng suite, entr utility, and some helper scripts.
https://github.com/redcode-labs/AirStrike
Automatically grab and crack WPA-2 handshakes with distributed client-server architecture.
Airstrike uses Hashcat Brain Architecture, aircrack-ng suite, entr utility, and some helper scripts.
https://github.com/redcode-labs/AirStrike
GitHub
GitHub - redcode-labs/AirStrike: Automatically grab and crack WPA-2 handshakes with distributed client-server architecture
Automatically grab and crack WPA-2 handshakes with distributed client-server architecture - redcode-labs/AirStrike
Forwarded from HackGit
Coraza WAF
OWASP Coraza is a golang enterprise-grade Web Application Firewall framework that supports Modsecurity's seclang language and is 100% compatible with OWASP Core Ruleset.
https://github.com/corazawaf/coraza
OWASP Coraza is a golang enterprise-grade Web Application Firewall framework that supports Modsecurity's seclang language and is 100% compatible with OWASP Core Ruleset.
https://github.com/corazawaf/coraza
GitHub
GitHub - corazawaf/coraza: OWASP Coraza WAF is a golang modsecurity compatible web application firewall library
OWASP Coraza WAF is a golang modsecurity compatible web application firewall library - corazawaf/coraza
Forwarded from Технологический Болт Генона
Для тех, кто питонами балуется Bloomberg открыл интересный тул
Memray is a memory profiler for Python
https://github.com/bloomberg/memray
Тред, который подглядел в @nocproject
https://twitter.com/1st1/status/1516859294896906241
Memray is a memory profiler for Python
https://github.com/bloomberg/memray
Notable features:+
- Traces every function call so it can accurately represent the call stack, unlike sampling profilers.
- Also handles native calls in C/C++ libraries so the entire call stack is present in the results.
- Blazing fast! Profiling causes minimal slowdown in the application. Tracking native code is somewhat slower, but this can be enabled or disabled on demand.
- It can generate various reports about the collected memory usage data, like flame graphs.
- Works with Python threads.
- Works with native-threads (e.g. C++ threads in native extensions)
Memray can help with the following problems:
- Analyze allocations in applications to help discover the cause of high memory usage.
- Find memory leaks.
- Find hotspots in code which cause a lot of allocations.
Тред, который подглядел в @nocproject
https://twitter.com/1st1/status/1516859294896906241
Когда-нибудь я соберу огромный пост из всех вот таких софтов, трюков и хаков,
Как обходить сетевые ограничения...
Как обходить сетевые ограничения...
Forwarded from Infrastructure Engineer🇺🇦
Friendship ended with
now
https://github.com/Nicocha30/ligolo-ng
proxychains + nmap now
ligolo + nmap is my best friendhttps://github.com/Nicocha30/ligolo-ng
GitHub
GitHub - nicocha30/ligolo-ng: An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface. - nicocha30/ligolo-ng