
Forwarded from DevOps&SRE Library
pyrra
Making SLOs with Prometheus manageable, accessible, and easy to use for everyone!https://github.com/pyrra-dev/pyrra
Phantun
A lightweight and fast UDP to TCP obfuscator.
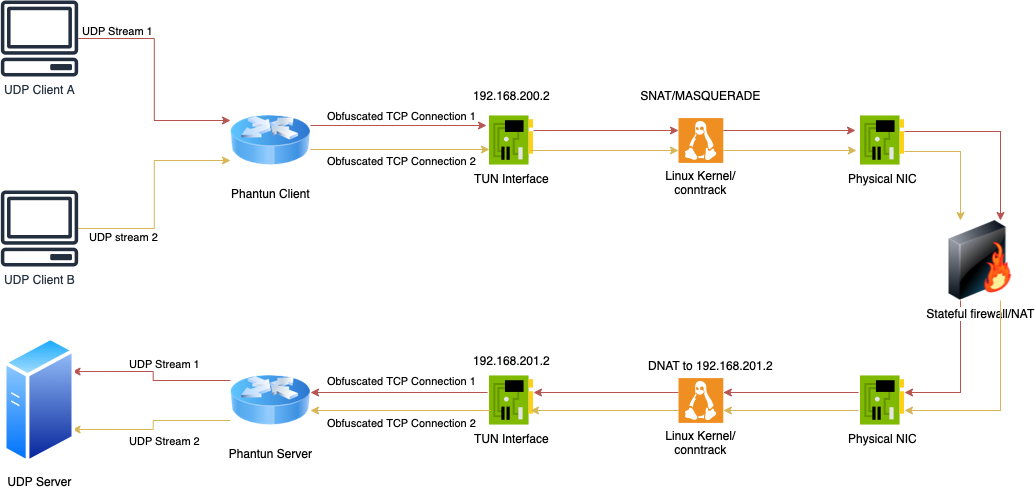
Project that obfuscated UDP packets into TCP connections. It aims to achieve maximum performance with minimum processing and encapsulation overhead.
It is commonly used in environments where UDP is blocked/throttled but TCP is allowed through.
Phantun simply converts a stream of UDP packets into obfuscated TCP stream packets. The TCP stack used by Phantun is designed to pass through most L3/L4 stateful/stateless firewalls/NAT devices. It will not be able to pass through L7 proxies. However, the advantage of this approach is that none of the common UDP over TCP performance killer such as retransmissions and flow control will occur. The underlying UDP properties such as out-of-order delivery are fully preserved even if the connection ends up looking like a TCP connection from the perspective of firewalls/NAT devices.
Phantun means Phantom TUN, as it is an obfuscator for UDP traffic that does just enough work to make it pass through stateful firewall/NATs as TCP packets.
https://github.com/dndx/phantun
Forwarded from Proxy Bar
Windows Privilege Escalation: SpoolFoolПатчили, фиксили CVE-2020-1048 и CVE-2020-1337, а дыра осталась.
Отличный разбор уязвимости CVE-2022-21999 («SpoolFool») в результате которой получаем права NT AUTHORITY\\SYSTEM. В статье рассмотрены 2 варианта атаки.
Как пролезть в мир принтеров без вазелина, расскажет расово верный индус Harshit Rajpal
Читаем тут.
#windows #LPE
Forwarded from HackGit
PixieWPS
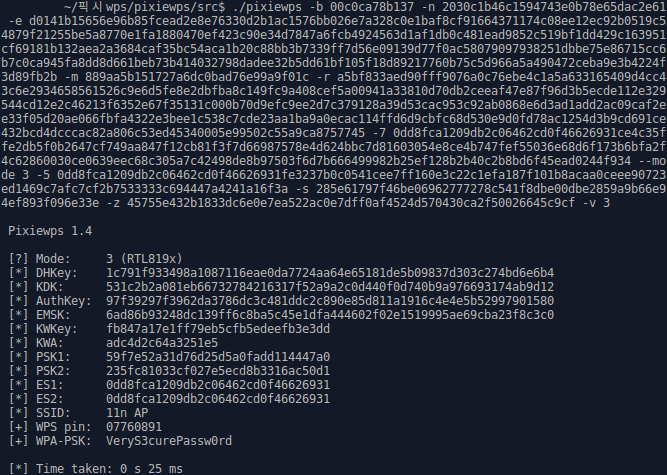
Tool written in C used to bruteforce offline the WPS PIN exploiting the low or non-existing entropy of some software implementations, the so-called "pixie-dust attack" discovered by Dominique Bongard in summer 2014. It is meant for educational purposes only.
As opposed to the traditional online brute-force attack, implemented in tools like Reaver or Bully which aim to recover the pin in a few hours, this method can get the PIN in only a matter of seconds or minutes, depending on the target, if vulnerable.
https://github.com/wiire-a/pixiewps
Forwarded from HackGit
Rucky
A simple to use USB #HID Rubber Ducky LaunchPad for #Android.
A USB HID Rubber Ducky Script All-In-One tool.
https://github.com/mayankmetha/Rucky
A simple to use USB #HID Rubber Ducky LaunchPad for #Android.
A USB HID Rubber Ducky Script All-In-One tool.
https://github.com/mayankmetha/Rucky
GitHub
GitHub - mayankmetha/Rucky: A simple to use USB HID Rubber Ducky Launch Pad for Android.
A simple to use USB HID Rubber Ducky Launch Pad for Android. - mayankmetha/Rucky
Forwarded from HackGit
Judge-Jury-and-Executable
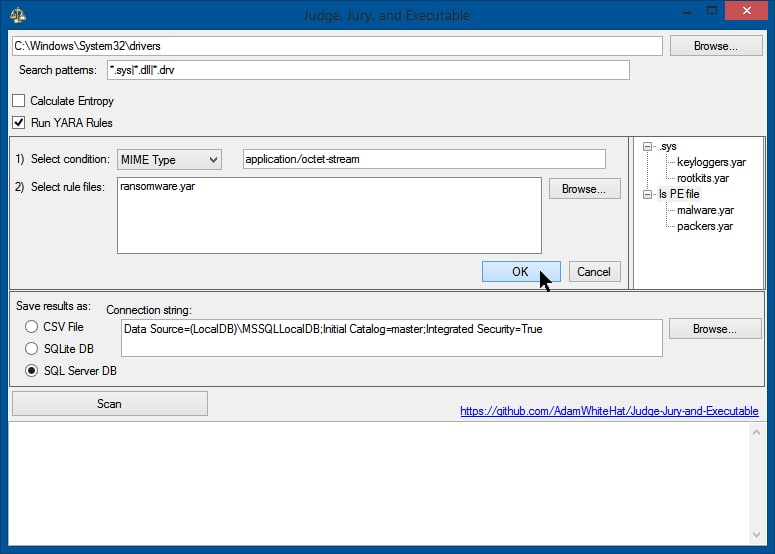
A file system forensics analysis scanner and threat hunting tool.
Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV. Threats and data can be probed harnessing the power and syntax of SQL.
Features:
▫️ Scan a mounted filesystem for threats right away
▫️ Or gather a system baseline before an incident, for extra threat hunting ability
▫️ Can be used before, during or after an incident
▫️ For one to many workstations
▫️ Scans the MFT, bypassing file permissions, file locks or OS file protections/hiding/shadowing
▫️ Up to 51 different properties gathered for every file
▫️ Scan results go into an SQL table for later searching, aggregating results over many scans and/or many machines, and historical or retrospective analysis
▫️ Leverage the power of SQL to search file systems, query file properties, answer complex or high-level questions, and hunt for threats or indicators of compromise
https://github.com/AdamWhiteHat/Judge-Jury-and-Executable
Forwarded from Devops Talks (Alex Green)
Uptime Kuma - It is a self-hosted monitoring tool like "Uptime Robot".
https://github.com/louislam/uptime-kuma
Прям советую 👆
https://github.com/louislam/uptime-kuma
Прям советую 👆
Forwarded from ATT&CK® COMMUNITY RUSSIA CHANNEL
Релиз WhaleHoney — honeypot на Flask, эмулирующий Docker API.
Jared Stroud (Lacework Labs) презентовал его в ходе доклада “ATT&CKing Containers in The Cloud”.
Ранее свой подход он описывал в статье Sand & Honey: Building Honeypots.
Jared Stroud (Lacework Labs) презентовал его в ходе доклада “ATT&CKing Containers in The Cloud”.
Ранее свой подход он описывал в статье Sand & Honey: Building Honeypots.
Forwarded from Linux и Линус
Secure software supply chains: good practices, at scale
Read: https://www.linuxfoundation.org/blog/secure-software-supply-chains-good-practices-at-scale/
Read: https://www.linuxfoundation.org/blog/secure-software-supply-chains-good-practices-at-scale/
Forwarded from ӉѦСҠіИԌ ҬЄѦӍ СѦИѦL ѺҒіСіѦL DіҒԱՏіóИ
x11docker
x11docker permite ejecutar aplicaciones gráficas de escritorio (y escritorios completos) en contenedores Docker
🔸Las herramientas de contenedores como Docker, podman y nerdctl permiten ejecutar aplicaciones en un entorno de contenedores aislado. Los contenedores requieren muchos menos recursos que las máquinas virtuales para tareas similares.
🔸Docker, podman y nerdctl no proporcionan un servidor de visualización para ejecutar aplicaciones con interfaz gráfica de usuario. x11docker llena el vacío. Ejecuta el servidor de visualización X en el sistema anfitrión y lo pone a disposición de los contenedores.
🔸Además, x11docker realiza algunos ajustes de seguridad para mejorar el aislamiento del contenedor y evitar las fugas de seguridad de X. Esto crea un entorno de caja de arena que es lo suficientemente bueno para proteger el sistema anfitrión de software potencialmente malicioso o con errores.
https://github.com/mviereck/x11docker
====================
Si encuentra software interesante, compártalo con la comunidad
GitHub
GitHub - mviereck/x11docker: Run GUI applications and desktops in docker and podman containers. Focus on security.
Run GUI applications and desktops in docker and podman containers. Focus on security. - mviereck/x11docker
Forwarded from HackGit
GitHub
GitHub - mebibite/springhound: Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring…
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and systems, allowing you to get insight on versions used. ...
Forwarded from Записки админа
🛠 If you’re not using SSH certificates you’re doing SSH wrong - об использовании аутентификации по сертификатам при работе по SSH. #ssh #напочитать
Forwarded from Записки админа
🔩 Ещё одна попытка создать песочницу для запуска чего угодно: https://github.com/containers/bubblewrap #sandbox #security #namespaces
Forwarded from Записки админа
👾 Интересный пример применения AI прямо в терминале с помощью ZSH плагина:
https://github.com/tom-doerr/zsh_codex
#zsh #openai #shell
https://github.com/tom-doerr/zsh_codex
#zsh #openai #shell
GitHub
GitHub - tom-doerr/zsh_codex: This is a ZSH plugin that enables you to use OpenAI's Codex AI in the command line.
This is a ZSH plugin that enables you to use OpenAI's Codex AI in the command line. - tom-doerr/zsh_codex
Forwarded from Записки админа
👾 Can Grafana run Doom? Просто Doom в Grafana, потому что могут, судя по всему.
Вот тут можно попробовать поиграть.
#grafana #doom
Вот тут можно попробовать поиграть.
#grafana #doom
Forwarded from Life-Hack - Хакер
Полезные шпаргалки для пентестеров и ИБ специалистов.
Шпаргалки являются отличным помощником при работе с определенным софтом или системой. С их помощью, ты сможешь прокачать свои навыки в определенной сфере и сократить время на выполнение задач для получения нужного результата.
• MITM cheatsheet.
• Active Directory Attack.md
• Active Directory penetration testing cheatsheet.
• Cloud - AWS Pentest.md
• Cloud - Azure Pentest.md
• Cobalt Strike - Cheatsheet.md
• Linux - Persistence.md
• Linux - Privilege Escalation.md
• Metasploit - Cheatsheet.md
• Methodology and enumeration.md
• Network Pivoting Techniques.md
• Network Discovery.md
• Reverse Shell Cheatsheet.md
• Subdomains Enumeration.md
• Windows - Download and Execute.md
• Windows - Mimikatz.md
• Windows - Persistence.md
• Windows - Post Exploitation Koadic.md
• Windows - Privilege Escalation.md
• Windows - Using credentials.md
• Best of Python Pentest Cheatsheet.
• Msfvenom Cheatsheet: Windows Exploitation.
• Best of OSCP Cheatsheet.
• Red Teaming and Social-Engineering CheatSheet.
• OSI Model Cheatsheet.
• Best of Red Teaming and Blue Teaming Cheatsheet.
• Best of iOS Forensics Cheatsheet.
• Best of Android Forensics Cheatsheet.
• Best of Digital Forensics Cheatsheet.
• Port Forwarding & Tunnelling Cheatsheet.
Forwarded from настенька и графики
Одна из моих самых любимых сеточек – карта науки. Сделана на данных пользователей научных порталов (что они смотрят, ищут, читают и тд). Получилась штука, очень классно показывающая междисциплинарность. Данным в исследовании уже больше 10 лет, но все равно нахожу ее очень интересной.
Forwarded from настенька и графики
Ну и вот такая по всем статьям, которые когда-либо публиковались в журнале Nature. Объемная, с визуализацией развития областей.