
Forwarded from Я все исправил к худшему (alekum)
https://positive.security/blog/send-my
Released an ESP32 firmware that turns the micocontroller into an (upload only) modem, and a macOS application to retrieve, decode and display the uploaded data:
https://github.com/positive-security/send-my
Released an ESP32 firmware that turns the micocontroller into an (upload only) modem, and a macOS application to retrieve, decode and display the uploaded data:
https://github.com/positive-security/send-my
positive.security
Send My: Arbitrary data transmission via Apple's Find My network | Positive Security
Apple AirTags: Arbitrary data can be uploaded from non-internet-connected devices by sending Find My BLE broadcasts to nearby Apple devices. We're releasing an ESP32 firmware that turns the microcontroller into an (upload only) modem, and a macOS application…
Forwarded from Offensive Xwitter
😈 [ ghostlulz1337, ghostlulz ]
If you want to learn more about Internal Pentesting & Red Teaming these are some really good resources
🔗 https://book.hacktricks.xyz/
🔗 https://www.thehacker.recipes/
🔗 https://ppn.snovvcrash.rocks/
🔗 https://cheats.philkeeble.com/
🔗 https://dmcxblue.gitbook.io/
🔗 https://www.vincentyiu.com/
🔗 https://www.ired.team/
🐥 [ tweet ]
Forwarded from GitHub Community
ShredOS – небольшой дистрибутив Linux с загрузкой через USB (BIOS или UEFI), единственной целью которого является безвозвратное стирание всего содержимого вашего компьютера с помощью программы nwipe
Если вы знакомы с dwipe из DBAN, тогда вы почувствуете себя как дома с ShredOS и nwipe
⤷ Ссылка на проект
GitHub | #Linux #Security #OS #Useful
Если вы знакомы с dwipe из DBAN, тогда вы почувствуете себя как дома с ShredOS и nwipe
⤷ Ссылка на проект
GitHub | #Linux #Security #OS #Useful

👍1
Forwarded from Ralf Hacker Channel (Ralf Hacker)
This media is not supported in your browser
VIEW IN TELEGRAM
Иногда нужно найти сайты/просканировать поддомены для определенного домена. Очень сильно помогает puredns.
1. Cначала запускаем dnsvalidator. Он соберёт список отвечающих NS серверов (остановить минут через 5 работы, 3-4к серверов хватит).
P.S. при сканировании с wi-fi, во время скана от сети отрубились все устройства, кроме сканирующего ноута😅
#pentest #scan #dns #soft #hacktricks
1. Cначала запускаем dnsvalidator. Он соберёт список отвечающих NS серверов (остановить минут через 5 работы, 3-4к серверов хватит).
dnsvalidator -tL https://public-dns.info/nameservers.txt -threads 100 -o resolvers.txt2. Затем запускаем puredns. Указываем словарь с поддоменами, домен для сканирования и файл, полученный на предыдущем шаге.
puredns bruteforce dns.lst domain.com -r resolvers.txtНа сканирование словарика 9.5 млн записей уйдет примерно 4 минуты))
P.S. при сканировании с wi-fi, во время скана от сети отрубились все устройства, кроме сканирующего ноута😅
#pentest #scan #dns #soft #hacktricks
Forwarded from HackGit
EvilCrowRF + Flipper Zero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
https://github.com/h-RAT/EvilCrowRF_Custom_Firmware_CC1101_FlipperZero
#infosec #pentesting #redteam
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
https://github.com/h-RAT/EvilCrowRF_Custom_Firmware_CC1101_FlipperZero
#infosec #pentesting #redteam
YouTube
EvilCrowRF - Firmware Web 2.0 beta
Device: ESP32 + 2xCC1101 / EvilCrowRF V2
https://github.com/h-RAT/
UPDATE:
- Flipper File Support
- Read RAW Protocol
- Read Princeton Protocol
- Read Holtek HT12X Protocol
- Read CAME Protocol
- Read CAME Protocol
- Read CAME Protocol
- Read CAME Protocol…
https://github.com/h-RAT/
UPDATE:
- Flipper File Support
- Read RAW Protocol
- Read Princeton Protocol
- Read Holtek HT12X Protocol
- Read CAME Protocol
- Read CAME Protocol
- Read CAME Protocol
- Read CAME Protocol…
Forwarded from HackGit
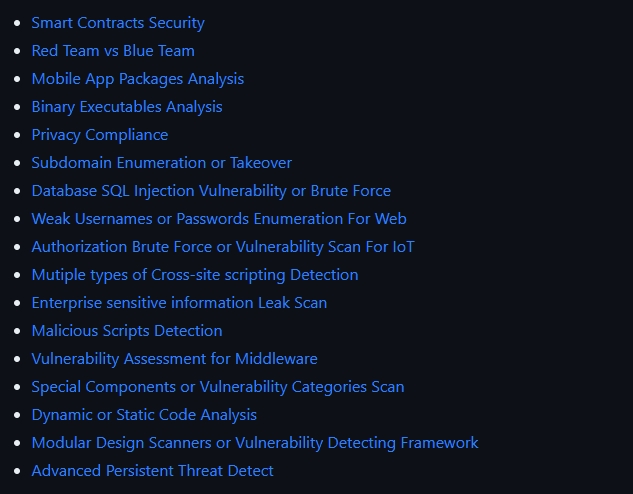
Scanners-Box
A powerful and open-source toolkit for hackers and security automation.
https://github.com/We5ter/Scanners-Box
#infosec #pentesting #redteam
A powerful and open-source toolkit for hackers and security automation.
https://github.com/We5ter/Scanners-Box
#infosec #pentesting #redteam
Forwarded from HackGit
nuclei_gpt
ChatGPT+Langchain+Nuclei Chat automates Nuclei template generation.
https://github.com/sf197/nuclei_gpt
#cybersecurity #infosec #bugbounty
ChatGPT+Langchain+Nuclei Chat automates Nuclei template generation.
https://github.com/sf197/nuclei_gpt
#cybersecurity #infosec #bugbounty

HackGit
nuclei_gpt ChatGPT+Langchain+Nuclei Chat automates Nuclei template generation. https://github.com/sf197/nuclei_gpt #cybersecurity #infosec #bugbounty
prompt_template="""You are an AI assistant for the open source library nuclei. The documentation is located at https://nuclei.projectdiscovery.io/templating-guide/.
You are given the following extracted parts of a long document and a question. Provide a answer with a yaml file to the documentation.
You should only use markdown file that are explicitly listed as a source in the context. Do NOT make up a yaml source code that is not listed.
Use the following pieces of context to answer the users question.
If you don't know the answer, just say that you don't know, don't try to make up an answer.
Question: {context}
=========
Answer:"""
👍1
Forwarded from Управление Уязвимостями и прочее
Бесплатный онлайн-курс по оффенсиву на 48 академических часов, да ещё и при поддержке Минцифры. Надо брать. Программа выглядит толково. Кажется хороший вариант для вкатывания в практическую ИБ без каких-либо затрат. Название правда правда такое себе. 🙄 Не люблю h-word, особенно в сочетании с маской Гая Фокса. Кажется от определенной атрибутики лучше держаться подальше, даже если это в шутку.
@avleonovrus #Минцифры #offensive
@avleonovrus #Минцифры #offensive
Forwarded from Админим с Буквой (Aleksandr Kondratev)
Victoriametrics релизнули продукт для сбора и визуализации логов. Интересно будет посмотреть-сравнить
https://docs.victoriametrics.com/VictoriaLogs/
https://github.com/VictoriaMetrics/VictoriaMetrics/releases/tag/v0.1.0-victorialogs
https://docs.victoriametrics.com/VictoriaLogs/
https://github.com/VictoriaMetrics/VictoriaMetrics/releases/tag/v0.1.0-victorialogs
Forwarded from Zhovner Hub
This media is not supported in your browser
VIEW IN TELEGRAM
Через дебаг лог во флиппере можно смотреть отладочные сообщения операционки устройства.
Тупо открываем сериал порт по USB и вводим команду
Тупо открываем сериал порт по USB и вводим команду
log debugForwarded from HackGit
msticpy
Microsoft Threat Intelligence Security Tools.
https://github.com/microsoft/msticpy
#cybersecurity #infosec
Microsoft Threat Intelligence Security Tools.
https://github.com/microsoft/msticpy
#cybersecurity #infosec

Forwarded from CyberSecurityTechnologies (-CST-)
#Analytics
OWASP Top 10 API Security Risks - 2023
https://owasp.org/API-Security/editions/2023/en/0x11-t10
OWASP Top 10 API Security Risks - 2023
https://owasp.org/API-Security/editions/2023/en/0x11-t10
Forwarded from Записки админа
This media is not supported in your browser
VIEW IN TELEGRAM
⚙️ Try - утилита, с помощью которой можно протестировать и проверить результат выполнения нужной команды. Для работы использует пространства имён и overlayfs.
https://github.com/binpash/try
#будничное #try #namespaces
https://github.com/binpash/try
#будничное #try #namespaces
Forwarded from Offensive Xwitter
😈 [ pdnuclei, nuclei ]
If you're not writing custom Nuclei templates, you're missing out! 😢
⚛️ In this blog post, we explore the power of nuclei custom templates and how creating your own is beneficial for users!
Don't miss out, read this 👇
🔗 https://blog.projectdiscovery.io/if-youre-not-writing-custom-nuclei-templates-youre-missing-out/
🐥 [ tweet ]
Forwarded from HackGit
🛡 VineShield
Obfuscation tool for all executing files and scripts written on python3
https://github.com/Nick-Vinesmoke/VineShield
#cybersecurity #infosec
Obfuscation tool for all executing files and scripts written on python3
https://github.com/Nick-Vinesmoke/VineShield
#cybersecurity #infosec

Semgrep rules for OWASP Mobile Application Security Testing Guide
https://github.com/mindedsecurity/semgrep-rules-android-security
https://github.com/mindedsecurity/semgrep-rules-android-security
GitHub
GitHub - OWASP/mastg: The OWASP Mobile Application Security Testing Guide (MASTG) is a comprehensive manual for mobile app security…
The OWASP Mobile Application Security Testing Guide (MASTG) is a comprehensive manual for mobile app security testing and reverse engineering. It describes technical processes for verifying the OWA...
Forwarded from PRO:PENTEST
Физический_пентест_Северная_Пальмира.pptx
365.9 MB
Презентация с моего выступления на Osint Workshop V "Миссия выполнима. Как происходят диверсии на объекте КИИ".
from North Palmyra with love
#Osint_report #NorthPalmyra
from North Palmyra with love
#Osint_report #NorthPalmyra
Forwarded from The Bug Bounty Hunter
Find authentication (authn) and authorization (authz) security bugs in web application routes.
https://github.com/mschwager/route-detect
https://github.com/mschwager/route-detect
GitHub
GitHub - mschwager/route-detect: Find authentication (authn) and authorization (authz) security bugs in web application routes.
Find authentication (authn) and authorization (authz) security bugs in web application routes. - mschwager/route-detect