
Forwarded from iMelnik
Часть софта из SysInternals. Теперь доступна и под Linux 😊
Process Explorer v17.03
PsTools v2.5
PsExec v2.42
PsPing v2.12
PsShutdown v2.6
Sysmon 1.1.1 for Linux
...
и другие 👉 Ссылка
#Linux #SisInternals
Process Explorer v17.03
PsTools v2.5
PsExec v2.42
PsPing v2.12
PsShutdown v2.6
Sysmon 1.1.1 for Linux
...
и другие 👉 Ссылка
#Linux #SisInternals
Forwarded from HackGit
Clairvoyance
Obtain GraphQL API schema even if the introspection is disabled.
https://github.com/nikitastupin/clairvoyance
#infosec #pentesting #bugbounty
Obtain GraphQL API schema even if the introspection is disabled.
https://github.com/nikitastupin/clairvoyance
#infosec #pentesting #bugbounty
Forwarded from HackGit
Awesome GPT + Security
A curated list of awesome security tools, experimental case or other interesting things with LLM or GPT.
https://github.com/cckuailong/awesome-gpt-security
#cybersecurity #infosec #pentesting
A curated list of awesome security tools, experimental case or other interesting things with LLM or GPT.
https://github.com/cckuailong/awesome-gpt-security
#cybersecurity #infosec #pentesting

Forwarded from S.E.Reborn
• Dorky is a command-line tool that searches GitHub and GitLab for matches in organization names, repository names, and usernames based on a list of input words. This tool can be helpful in identifying potential targets for security assessments, finding interesting projects, and discovering new organizations and users on GitHub and GitLab.
• https://github.com/codingo/dorky
#OSINT
Please open Telegram to view this post
VIEW IN TELEGRAM
GitHub
GitHub - codingo/dorky: A tool to quickly do keyword searches over Gitlab and Github for OSINT & bug bounty recon
A tool to quickly do keyword searches over Gitlab and Github for OSINT & bug bounty recon - codingo/dorky
👍1
Forwarded from k8s (in)security (r0binak)
Metarget – это инструмент, позволяющий разворачивать уязвимые инфраструктуры в одну команду.
Развертывание инфраструктуры занимает довольно много времени и часто это становится проблемой при тестировании
Вообщем, если вам нужна уязвимая версия
Самое то, чтобы тренировать и отрабатывать навыки для пентестов.
Развертывание инфраструктуры занимает довольно много времени и часто это становится проблемой при тестировании
PoC. Конечно, есть такие проекты как Vulhub или VulApps, но они всё-такие заточены на уязвимые веб-приложения, которые нужно обернуть в контейнер для удобного использования.Вообщем, если вам нужна уязвимая версия
docker или Kubernetes, то эта тулза musthave. Вот что она предлагает:- уязвимости в docker
- уязвимости в ядре
- уязвимости в containerd
- уязвимости в runc
- уязвимости и мисконфиги в kubernetesСамое то, чтобы тренировать и отрабатывать навыки для пентестов.
Forwarded from HackGit
DeepSecrets
A better tool for secret scanning.
DeepSecrets expands classic regex-search approaches with semantic analysis, dangerous variable detection, and more efficient usage of entropy analysis. Code understanding supports 500+ languages and formats and is achieved by lexing and parsing - techniques commonly used in SAST tools.
https://github.com/avito-tech/deepsecrets
#infosec #pentesting #bugbounty
Forwarded from HackGit
al-khaser
A PoC "malware" application with good intentions that aims to stress your anti-malware system. It performs a bunch of common malware tricks with the goal of seeing if you stay under the radar.
https://github.com/LordNoteworthy/al-khaser
#malware #infosec #pentesting
A PoC "malware" application with good intentions that aims to stress your anti-malware system. It performs a bunch of common malware tricks with the goal of seeing if you stay under the radar.
https://github.com/LordNoteworthy/al-khaser
#malware #infosec #pentesting

Forwarded from HackGit
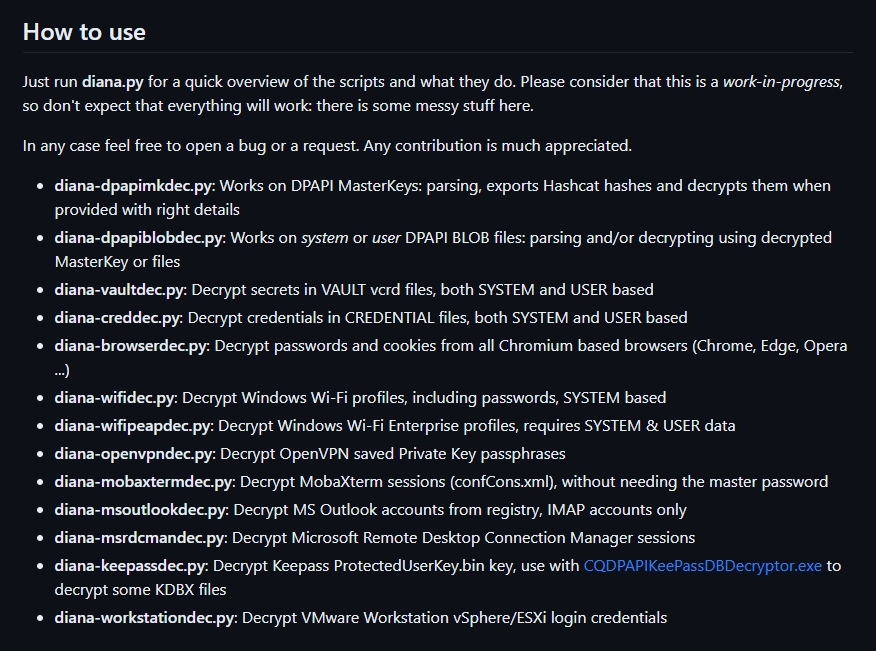
DIANA
Credential Recovery Framework.
https://github.com/tijldeneut/diana
#infosec #pentesting #redteam
Credential Recovery Framework.
https://github.com/tijldeneut/diana
#infosec #pentesting #redteam
Forwarded from Cybred
Репозиторий с огромным списком PoC'ов для многих CVE, начиная с 2008 года https://github.com/nomi-sec/PoC-in-GitHub.
Автонаполняемый, существует отдельный сайт https://poc-in-github.motikan2010.net/.
Автонаполняемый, существует отдельный сайт https://poc-in-github.motikan2010.net/.
GitHub
GitHub - nomi-sec/PoC-in-GitHub: 📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware. - nomi-sec/PoC-in-GitHub
Forwarded from HackGit
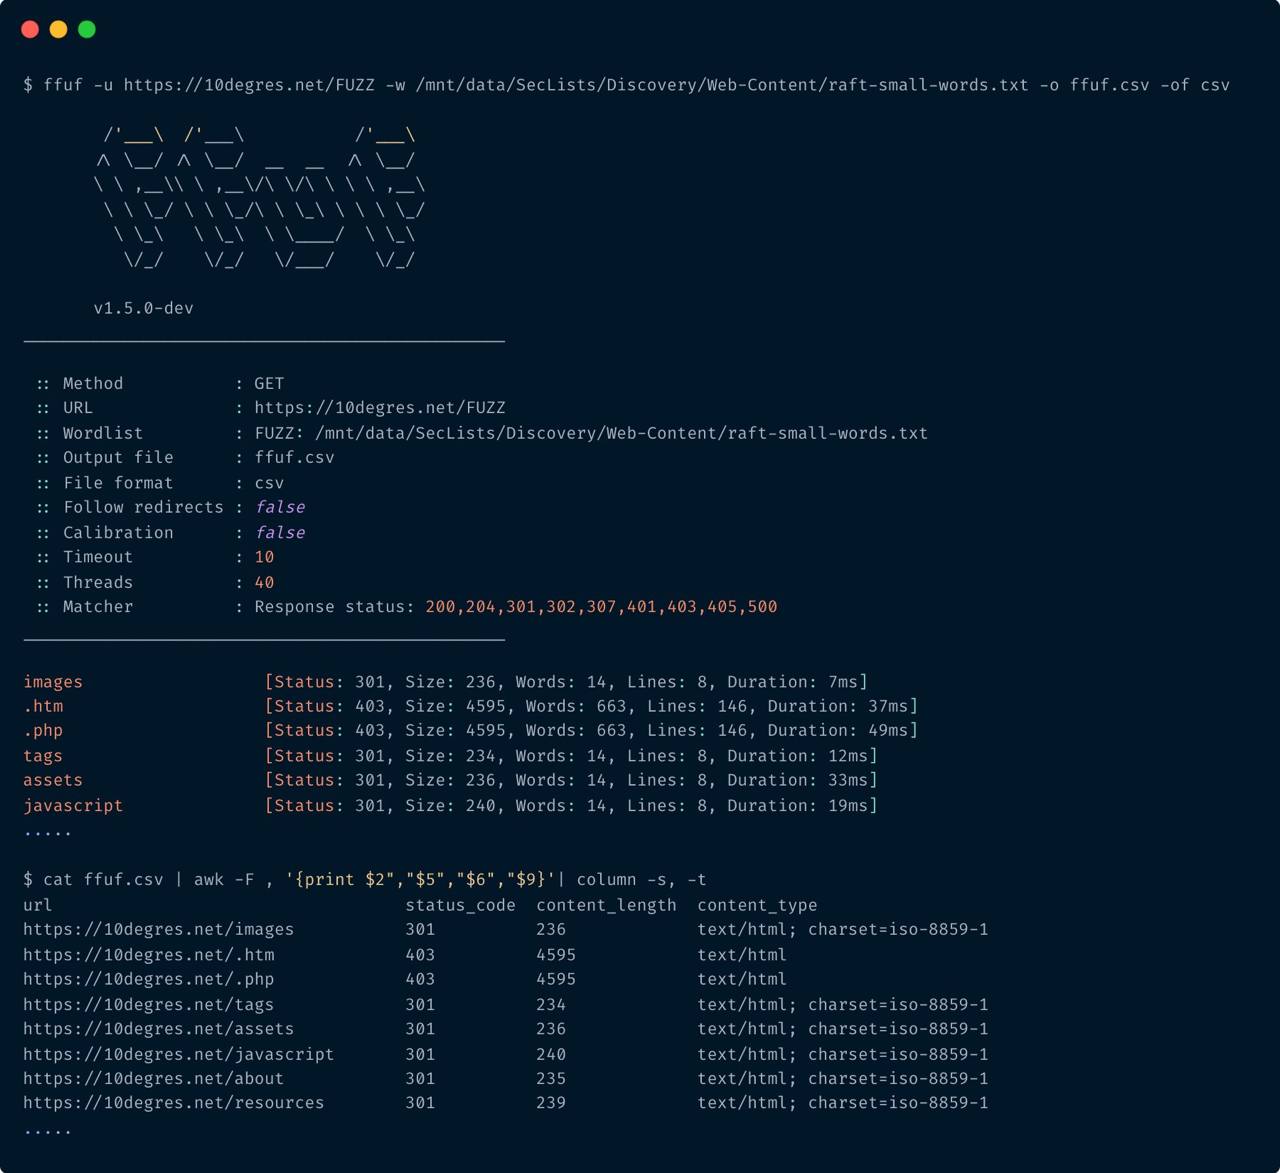
ReconBulk
Automated Subdomain Enumeration and Scanning Tool
This script automates the process of subdomain enumeration and scanning using several popular open-source tools, combining their results and providing detailed output. The primary purpose of this tool is to simplify and streamline the process of discovering subdomains and their related information for a given domain.
https://github.com/TaurusOmar/reconbulk
#infosec #pentesting #bugbounty
Forwarded from HackGit
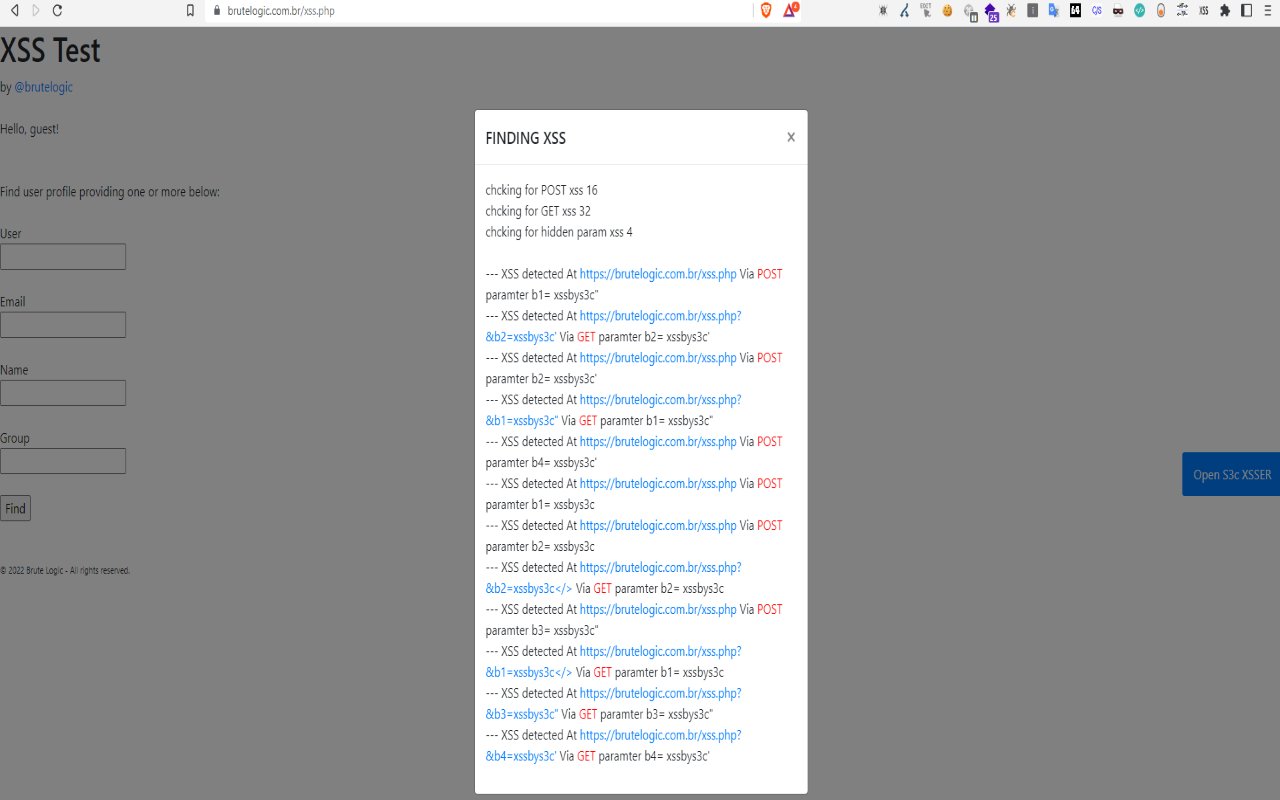
s3cXSSer
This extension will help you to detect GET/POST based XSS vulnerability in any website easily.
https://github.com/s3c-krd/s3cXSSer
#infosec #pentesting #bugbounty
This extension will help you to detect GET/POST based XSS vulnerability in any website easily.
https://github.com/s3c-krd/s3cXSSer
#infosec #pentesting #bugbounty
OWASP API Security Top 10 2023
https://github.com/OWASP/API-Security/tree/master/2023/en/src
https://github.com/OWASP/API-Security/tree/master/2023/en/src