
Forwarded from ANTICHAT Channel
Современный PHP уже не про магические кавычки. Ругать его сейчас практически не за что. Тем не менее, популярность и низкий порог входа делают своё. И много кодеров, до сих пор, продолжают тянуть устаревшую жуть языка.
С одной из них, приходится сталкиваться время от времени. Ею является эмуляция Register Globlas. То ли из-за банальной лени, то ли из-зараспиздяйства , разработчиком в проект добавляется костыль аля extract($_GET) или $$v в цикле. Например:
Ответ:https://expressionengine.com/?protected=1&_SERVER=1
Вот так, гвозди можно забивать микроскопом. Но как всегда, во всём обвинят PHP 🤷♂️
С одной из них, приходится сталкиваться время от времени. Ею является эмуляция Register Globlas. То ли из-за банальной лени, то ли из-за
https://expressionengine.com/?this=1К чему такие финты приводят, можно почитать на нашем форуме - $this - это специальная переменная. А теперь взгляните на скриншот и попробуйте найти уязвимость.
https://www.whmcs.com/members/?this=1
https://www.1c-bitrix.ru/auth/?this=1
Ответ:
Вот так, гвозди можно забивать микроскопом. Но как всегда, во всём обвинят PHP 🤷♂️
Forwarded from Cyber Detective
"Learn Regex in 4 tweets"
I started using regular expressions years ago, but learning them is a never-ending process😀
Today I found a thread from
@s0md3v
that explains cool how to use #regexp. https://twitter.com/s0md3v/status/1171394403065155584
I decided to keep it for myself and make it into a table
I started using regular expressions years ago, but learning them is a never-ending process😀
Today I found a thread from
@s0md3v
that explains cool how to use #regexp. https://twitter.com/s0md3v/status/1171394403065155584
I decided to keep it for myself and make it into a table
Forwarded from Open Source
RustDesk for Android
Популярное приложение для удаленного рабочего стола с открытым исходным кодом, альтернатива TeamViewer, теперь для Android.
▫️Чтобы удаленное устройство могло управлять вашим Android-устройством RustDesk использует API AccessibilityService для реализации удаленного управления Addroid.
▫️В дополнение к удаленному управлению вы также можете легко передавать файлы между устройствами Android и ПК с помощью RustDesk.
▫️Вы можете использовать сервер разработчика для рандеву/ретрансляции или собственный хостинг.
https://github.com/rustdesk/rustdesk
Документация: https://rustdesk.com/docs/en/manual/mobile/
F-droid: https://f-droid.org/packages/com.carriez.flutter_hbb/

👍2
Хорошая статья для новичков.
Все по полочкам с реальными советами, которые работают, если есть желание ворваться 👨🏭
Все по полочкам с реальными советами, которые работают, если есть желание ворваться 👨🏭
Forwarded from ANTICHAT Channel
Отличная подборка RCE уязвимостей. Жаль видео на французском, верните мне мой 18 век ;( Но автор также выложил слайды, что тоже ничего.
https://www.youtube.com/watch?v=Z9GN6cuggYQ
https://www.youtube.com/watch?v=Z9GN6cuggYQ
Forwarded from Evil Technologies (Mr. Anderson 🇺🇦)
Flipper Zero это портативный инструмент для пентестеров и гиков. Он совмещает в себе множество функций в небольшом корпусе.
А вот статейка про написание софта под Flipper Zero:
https://telegra.ph/razrabotka-prostogo-prilozheniya-pod-Flipper-Zero-05-15
Thanks to @c4nc7
А вот статейка про написание софта под Flipper Zero:
https://telegra.ph/razrabotka-prostogo-prilozheniya-pod-Flipper-Zero-05-15
Thanks to @c4nc7
Forwarded from GitHub repos
dair-ai/MLOPs-Primer
A collection of resources to learn about MLOPs.
Stars: 555 Issues: 0 Forks: 26
https://github.com/dair-ai/MLOPs-Primer
A collection of resources to learn about MLOPs.
Stars: 555 Issues: 0 Forks: 26
https://github.com/dair-ai/MLOPs-Primer
GitHub
GitHub - dair-ai/MLOPs-Primer: A collection of resources to learn about MLOPs.
A collection of resources to learn about MLOPs. Contribute to dair-ai/MLOPs-Primer development by creating an account on GitHub.
Forwarded from GitHub repos
yandex/YaLM-100B
Pretrained language model with 100B parameters
Language: Python
Stars: 1664 Issues: 9 Forks: 109
https://github.com/yandex/YaLM-100B
Pretrained language model with 100B parameters
Language: Python
Stars: 1664 Issues: 9 Forks: 109
https://github.com/yandex/YaLM-100B
GitHub
GitHub - yandex/YaLM-100B: Pretrained language model with 100B parameters
Pretrained language model with 100B parameters. Contribute to yandex/YaLM-100B development by creating an account on GitHub.
Forwarded from ANTICHAT Channel
How would an attacker remotely take over a personal Linux or Android device? Send a malicious link and get code execution through the browser? Or target a messenger or an email client? Well, how about sending a series of network packets and owning the kernel directly 😋В статье описан метод фаззинга ядра Linux, в процессе работы с транспортными протоколами. Для поиска багов и впоследствии, если "повезёт", RCE уязвимостей. То, что для простого обывателя кажется фантастикой, тут обсуждается в обыденном ключе и даже вскользь упоминается такая уязвимость в прошлом 😱 Проще говоря, предлагается попробовать нафармить крякер интернета, на полном серьёзе 😎 Инфографика, много исходного кода, крутое оформление - их есть там. Просто мозгодробительный ресёрч 🤯
Andrey Konovalov
🔍 Looking for Remote Code Execution bugs in the Linux kernel
Using syzkaller to fuzz the Linux kernel network stack externally
Forwarded from ANTICHAT Channel
Этот скрипт используется для автоматизации некоторых монотонных действий. И влючает в себя следующую цепочку:
■ брут и поиск поддоменов таргета, используя assetfinder, Sublist3r, subfinder и amass
■ фильтрация живых доменов из полученного списка поддоменов
■ извлечение тайтлов с помощью httpx
■ сканирование на Subdomain Takeover с помощью nuclei
■ использование gauplus и gf для извлечения параметров и адресов
■ проверка на низко висящие XSS, SSTI, SSRF, SQLi и т.п.
■ сохранение всего этого дела в текстовый файл
■ уведомление об окончании работы
Звучит многообещающе, будем посмотреть 🧐
https://github.com/R0X4R/Garud
Forwarded from S4n6c7u4ry_labs (Aaaa)
Я некоторое время назад обещал статьи про SQLI. Продолжаю исполнять обещания, на повестке подборка материалов для вката в смарт контракты и их ломание.
1.https://github.com/OffcierCia/DeFi-Developer-Road-Map роадмап по разработке от Oficer CIA оч крутой мужик , мейн языки Solidity, JS, Python, про гит и линукс молчу. Гуглим в инетах пет проекты и ебашим. Про IDE поговорим отдельно.
2. Если мы набили руку, то идем и гуглим DASP 10 или почему web 3 дырявый как антивир касперского (гыг типо щютка)
3. Если вы выполнили предыдущие 2 пункта, то этот для вас. Да ктф говно. Да я в курсе что я пидор. Да когда нибудь я выпущу материал про обфускацию. Но у вас нет других путей у вас нет. Подбор цтф тасок на смарт контракты, типо hack the box( будет пополняться)
Capture the Ether
• The Ethernaut
• Etherhack
• Security Innovation Blockchain CTF
• Ciphershastra CTF
• Defi Hack
• Gacha Lab (BSC Testnet)
• Cipher Shastra
3. Можете искать дыры теперь в смарт контрактах на бб площадке http://immunefi.com
4. Тулсет
1. Browser based Solidity IDE: [http://remix.ethereum.org/](http://remix.ethereum.org/)
2. Securify V2.0: [https://github.com/eth-sri/securify2](https://github.com/eth-sri/securify2)
3. Oyente: [https://github.com/enzymefinance/oyente](https://github.com/enzymefinance/oyente)
4. The Hydra Aplha: [https://github.com/IC3Hydra/Hydra](https://github.com/IC3Hydra/Hydra)
5. Porosity: [https://github.com/msuiche/porosity](https://github.com/msuiche/porosity)
6. Manticore: [https://github.com/trailofbits/manticore/](https://github.com/trailofbits/manticore/)
7. Etherplays: [https://github.com/crytic/ethersplay](https://github.com/crytic/ethersplay)
8. Online Solidity Decompiler: [https://ethervm.io/decompile](https://ethervm.io/decompile)
9. Mythril: [https://github.com/ConsenSys/mythril](https://github.com/ConsenSys/mythril)
10. Echidna: [https://github.com/crytic/echidna](https://github.com/crytic/echidna)
11. Slither: [https://github.com/trailofbits/slither](https://github.com/trailofbits/slither)
12. Плагин solidity для VSC
13. Плагин solidity для Vim и Emacs.
Говорю сразу мне довольно тяжело писать свои статьи/заметки, поэтому поливать дерьмом меня не надо. Щас я сижу над 3 материалами, один из которых солью в паблик. В начале июля думаю постримить и разобрать основные уязвимости на твиче/ютубе. Я в курсе что обещал выпустить материал про реверс апк и про разбор одной из уязвимостей, но бля я стулент и только сдал сессию, а на неделе еще защита диплома.
GitHub
GitHub - OffcierCia/DeFi-Developer-Road-Map: DeFi Developer roadmap is a curated Developer handbook which includes a list of the…
DeFi Developer roadmap is a curated Developer handbook which includes a list of the best tools for DApps development, resources and references! - OffcierCia/DeFi-Developer-Road-Map
Forwarded from HackGit
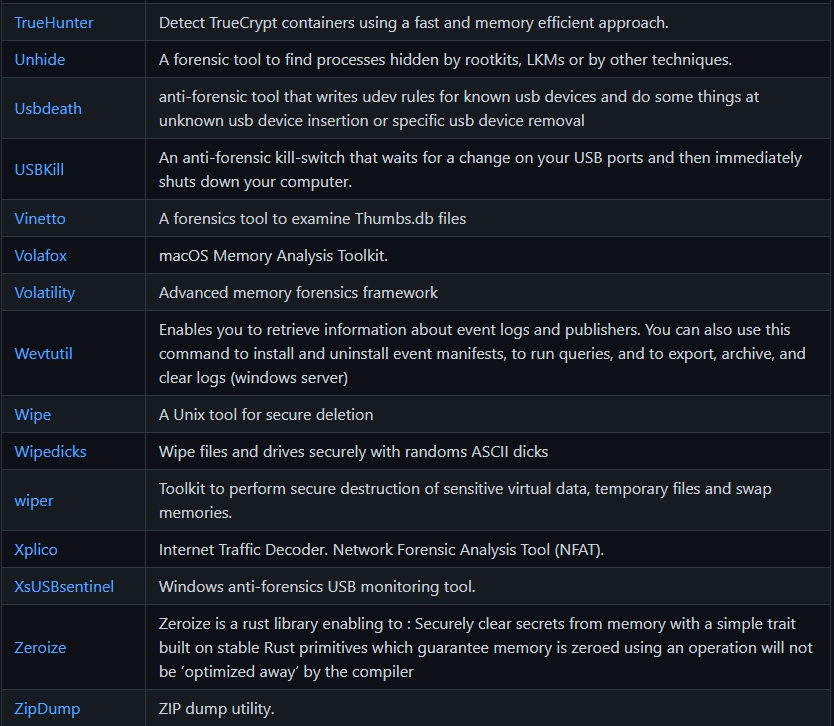
Awesome-anti-forensic
Tools and packages that are used for countering forensic activities, including encryption, steganography, and anything that modify attributes.
This all includes tools to work with anything in general that makes changes to a system for the purposes of hiding information.
https://github.com/shadawck/awesome-anti-forensic
#forensic
Forwarded from Linux и Линус
Deepin system startup process and introduction of key components [1]
Runlevel
Which services are started when the system starts is determined by the run level. The systemd service will specify which target to run in. These targets usually correspond to the target of the run level. If NetworkManager is started at the m...
Read: https://deepinlinux.hashnode.dev/deepin-system-startup-process-and-introduction-of-key-components-1
Forwarded from ANTICHAT Channel
Advanced SQL Injection Cheatsheet
MySQL Injection Cheatsheet
MySQL Injection Cheatsheet
• Error- or UNION-based SQLi
   • Routed queries (Advanced WAF Bypass)
   • Bypass Error: The used SELECT statements have a different number of columns
   • New attacking vectors (Bypassing WAF)
      • The Alternative way of using And 0
      • The Alternative WAY of using Null
   • Boolean-based (content-based) Blind SQLi
   • Time Based SQLi
   • Stabilise & Whitespace Filter Bypass
   • Local File Inclusion (LFI)
   • Privilege Escalation
PostgreSQL Injection Cheatsheet • Error- or UNION-based SQLi
• Local File Inclusion (LFI)
• Privilege Escalation
Oracle Injection Cheatsheet • Error- or UNION-based SQLi
MSSQL Injection Cheatsheet • Error- or UNION-based SQLi
• Privilege EscalationForwarded from Linux и Линус
Deepin system startup process and introduction of key components [2]
System components are divided into system-level components and user-level components according to the user at startup. System-level components have nothing to do with users and are generally started before the user logs in, while user-level component...
Read: https://deepinlinux.hashnode.dev/deepin-system-startup-process-and-introduction-of-key-components-2
Forwarded from HackGit
Dismember
Dismember is a command-line toolkit for Linux that can be used to scan the memory of all processes (or particular ones) for common secrets and custom regular expressions, among other things.
It will eventually become a full /proc toolkit.
https://github.com/liamg/dismember
@HackGit
Dismember is a command-line toolkit for Linux that can be used to scan the memory of all processes (or particular ones) for common secrets and custom regular expressions, among other things.
It will eventually become a full /proc toolkit.
https://github.com/liamg/dismember
@HackGit